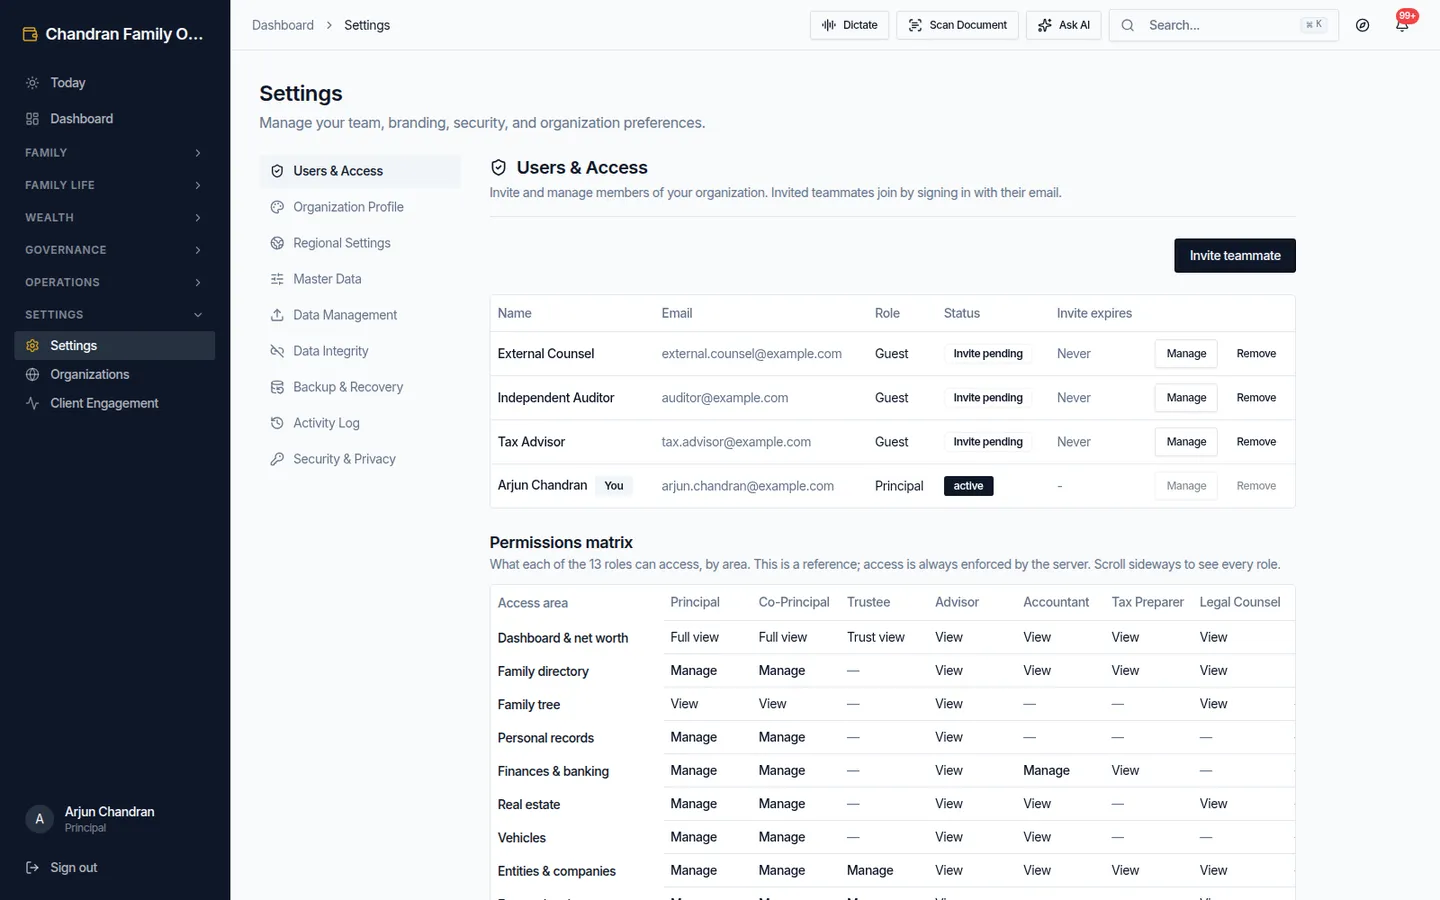
Thirteen roles, two-factor enforcement and a complete audit trail
Role-based access across 13 roles, app-enforced 2FA with passkeys, full client isolation and an audit log of every change.
Settings — security, roles, branding and reference data
How it works
Access is governed by thirteen roles — from Principal with full control to time-limited Guests who see only their data room. Every screen and every record type is gated by role, so each person sees exactly what their responsibility requires.
Security is enforced in the application itself: two-factor authentication with authenticator apps and passkeys, recovery codes, and session management that lets the principal review and revoke active sessions.
Every client's data is fully isolated from every other, uploads are partitioned per client in object storage, and every change to every record is written to an immutable audit trail — attributed, timestamped and reviewable.
Capabilities
13 access roles
From Principal to Guest, each role sees exactly what it should.
2FA & passkeys
App-enforced TOTP, passkeys and recovery codes.
Session control
Review and revoke active sessions at any time.
Complete audit trail
Every change attributed and reviewable — nothing off the record.
Full client isolation
Each family's data and documents are fully separated.
Private branding
Your own name, logo and colors on your family's workspace.
 FamVault